
Certifications
XOne is certified under Spain's National Security Framework (ENS), medium category, and ISO/IEC 27001:2022 by an accredited certification body.
At XOne (COMPUTER GLOBAL SOFTWARE, S.L.), information security is a business requirement, not an add-on. The information system that supports our mobile application development and publishing service is certified under the Esquema Nacional de Seguridad (ENS), Spain’s National Security Framework, and the ISO/IEC 27001:2022 standard, both by an accredited certification body.
On this page
- Certification of Conformity with the Esquema Nacional de Seguridad (ENS) – Royal Decree 311/2022
- ISO/IEC 27001:2022 Certification – Information Security
- Information Security Policy
Certification of Conformity with the Esquema Nacional de Seguridad (ENS)
COMPUTER GLOBAL SOFTWARE, S.L. holds the Certificate of Conformity with the Esquema Nacional de Seguridad in the MEDIUM category, having been audited and found compliant with the requirements of Royal Decree (Real Decreto) 311/2022, of May 3, which regulates the Esquema Nacional de Seguridad.
- Certificate number: ENS_2.026.126
- Security category: MEDIUM — MEDIUM level in all five dimensions (Availability, Integrity, Confidentiality, Authenticity and Traceability), with 64 security measures implemented.
- Scope: information system supporting the mobile application development and publishing service.
- Location: Parque Científico y Tecnológico de Extremadura (PCTEX) building, Avenida de Elvas, Campus Universitario, Badajoz — with its own data center.
- Statement of applicability: version 1.1, dated February 11, 2026.
- Certification body: ACCM — Agencia para la Certificación de la Calidad y el Medio Ambiente, S.L., accredited by ENAC (Spain’s National Accreditation Body).
- Date granted: August 9, 2026
- Valid until: August 9, 2028
View the ENS certificate (PDF)
Conformity badge published in accordance with Article 38 of Royal Decree 311/2022.
ISO/IEC 27001:2022 Certification
COMPUTER GLOBAL SOFTWARE, S.L. has an Information Security, Cybersecurity and Privacy Protection Management System certified under the ISO/IEC 27001:2022 standard.
- Registration code: SI-623926
- Standard: ISO/IEC 27001:2022
- Scope: Information Security Management System supporting mobile application development and publishing services.
- Location: Avda. de Elvas, s/n — 06006 Badajoz.
- Certification body: ACCM — Agencia para la Certificación de la Calidad y el Medio Ambiente.
- First issued: April 10, 2026
- Current issue: April 10, 2026
- Valid until: April 9, 2029
View the ISO/IEC 27001 certificate (PDF)

Information Security Policy
COMPUTER GLOBAL SOFTWARE, S.L. — Document Org.1. Edition 01, dated February 11, 2026. Approved by Management.
1. Purpose and implementation
COMPUTER GLOBAL SOFTWARE, S.L., as a company dedicated to the Information System supporting the MOBILE APPLICATION DEVELOPMENT AND PUBLISHING SERVICE, in order to offer all its stakeholders the highest guarantees regarding the security of the information used.
In view of all the above, Management establishes the following information security objectives:
- Provide a framework to increase resilience in order to respond effectively.
- Ensure the fast and efficient recovery of services in the event of any physical disaster or contingency that may occur and put the continuity of operations at risk.
- Prevent information security incidents to the extent technically and economically feasible, and mitigate the information security risks generated by our activities.
- Guarantee the confidentiality, integrity, availability, authenticity and traceability of information.
To achieve these objectives, it is necessary to:
- Continuously improve our information security system.
- Comply with applicable legal requirements and any other requirements to which we subscribe, in addition to the commitments made to customers, and keep them continuously up to date. The legal and regulatory framework in which we carry out our activities is:
- REGULATION (EU) 2016/679 OF THE EUROPEAN PARLIAMENT AND OF THE COUNCIL of April 27, 2016 on the protection of natural persons with regard to the processing of personal data and on the free movement of such data.
- Ley Orgánica 3/2018, of December 5, on the Protection of Personal Data and Guarantee of Digital Rights (Spain’s Organic Data Protection Law).
- Real Decreto Legislativo 1/1996, of April 12, Intellectual Property Law (Ley de Propiedad Intelectual).
- Real Decreto-ley 2/2018, of April 13, amending the consolidated text of the Intellectual Property Law.
- Royal Decree 3/2010, of January 8, implementing the Esquema Nacional de Seguridad, as amended by Royal Decree 951/2015, of October 23.
- UNE-EN ISO/IEC 27001 standard for information security.
- Law 34/2002, of July 11, on Information Society Services and Electronic Commerce (LSSI).
- Royal Decree 3/2010, of January 8, regulating the Esquema Nacional de Seguridad in the field of e-Government.
- Royal Decree 311/2022, of May 3, regulating the Esquema Nacional de Seguridad.
- Identify potential threats, as well as the impact that such threats, should they materialize, could have on business operations.
- Preserve the interests of its main stakeholders (customers, shareholders, employees and suppliers), its reputation, its brand and its value-creating activities.
- Work together with our suppliers and subcontractors to improve the provision of IT services, service continuity and information security, resulting in greater efficiency in our activity.
- Assess and ensure the technical competence of staff, and ensure their proper motivation to take part in the continuous improvement of our processes, providing the appropriate training and internal communication so that they develop the good practices defined in the system.
- Ensure the proper condition of facilities and appropriate equipment, so that they are in line with the company’s activity, objectives and goals.
- Ensure the continuous analysis of all relevant processes, establishing the appropriate improvements in each case, based on the results obtained and the objectives set.
- Structure our management system so that it is easy to understand. Our management system has the following structure:
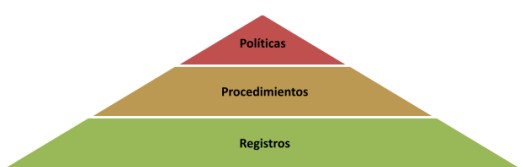
Management of our system is entrusted to the IT Systems Manager, and the system will be available in our information system in a repository, which can be accessed according to the access profiles granted under our current access management procedure.
2. ENS basic principles
The security policy of COMPUTER GLOBAL SOFTWARE, S.L. will be established in accordance with the basic principles set out in Chapter II and will be implemented by applying the following minimum requirements:
- a) Organization and implementation of the security process.
- b) Risk analysis and management.
- c) Personnel management.
- d) Professionalism.
- e) Access authorization and control.
- f) Protection of facilities.
- g) Acquisition of security products and procurement of security services.
- h) Least privilege.
- i) System integrity and updating.
- j) Protection of stored information and information in transit.
- k) Prevention with respect to other interconnected information systems.
- l) Activity logging and detection of malicious code.
- m) Security incidents.
- n) Business continuity.
- ñ) Continuous improvement of the security process.
3. Security organization
The essential responsibility lies with the organization’s General Management, since it is responsible for organizing duties and responsibilities and for providing adequate resources to achieve the objectives of the ENS and ISO27001. Executives are also responsible for setting a good example by following the established security rules.
These principles are adopted by Management, which provides the necessary means and gives its employees sufficient resources to comply with them, setting them out and making them public through this Integrated Management Systems Policy.
The defined security roles or functions are:
| Role | Duties and responsibilities |
|---|---|
| Information Owner Rubén Montero (RINF) | Make decisions regarding the information processed |
| Service Owner Rubén Montero (RSER) | Coordinate the implementation of the system Continuously improve the system |
| Security Officer Rubén Montero (RSEG) | Determine the suitability of technical measures Provide the best technology for the service |
| Systems Manager Luis Lozano (RSIS) | Coordinate the technical implementation of the system Continuously improve the system |
| Management Rubén Montero (DIR) | Provide the resources the system needs Lead the system |
| Management System Manager José María Cabezas (RSG) | Coordinate the implementation of the ENS management system |
This definition is completed in the job profiles and in the system documents.
The procedure for their appointment and renewal will be ratification by the security committee.
The committee for security management and coordination is the body with the highest responsibility within the information security management system, so all the most important security-related decisions are agreed by this committee. The members of the information security committee are:
- Information Security Management System Managers
- Company Management (partner-directors)
Duties and responsibilities of the security committee.
The duties and responsibilities of the security committee are defined in the «Security Committee Constitution Minutes».
Security committee renewal period.
The members of the security committee will be ratified or replaced annually, at the committee’s own meeting.
These members are appointed by the committee, the only body that can appoint, renew and remove them.
The security committee is an autonomous, executive body with decision-making autonomy that does not have to subordinate its activity to any other part of our company.
4. Risk management
All systems subject to this Policy must carry out a risk analysis, assessing the threats and risks to which they are exposed. This analysis is reviewed regularly:
- at least once a year;
- when the information handled changes;
- when the services provided change;
- when a serious security incident occurs;
- when serious vulnerabilities are reported.
To harmonize risk analyses, the Security Committee will establish a reference valuation for the different types of information handled and the different services provided. The Security Committee will promote the availability of resources to meet the security needs of the different systems, encouraging cross-cutting investments.
The risk analysis will take into account the risk analysis methodology developed in procedure Op.pl.1 Risk Analysis.
5. Personnel management
All members of COMPUTER GLOBAL SOFTWARE, S.L. are obliged to know and comply with this Information Security Policy and the Security Regulations, and the Security Committee is responsible for providing the necessary means for the information to reach those affected.
All members of COMPUTER GLOBAL SOFTWARE, S.L. will attend a security awareness session at least once a year. A continuous awareness program will be established to cover all members of COMPUTER GLOBAL SOFTWARE, S.L., in particular new hires.
People with responsibility for the use, operation or administration of systems will receive training in the secure handling of systems to the extent they need it to do their job. Training will be mandatory before taking on a responsibility, whether it is their first assignment or a change of job or of responsibilities within it.
6. Professionalism and human resources security
The objectives of controlling personnel security are:
- Reduce the risks of human error, irregularities, misuse of facilities and resources, and unauthorized handling of information.
- Explain security responsibilities at the recruitment stage, include them in the agreements to be signed and verify compliance with them while the employee performs their duties.
- Ensure that users are aware of information security threats and concerns and are trained to support the organization’s Information Security Policy in the course of their normal duties.
- Establish confidentiality commitments with all staff and users outside the information processing facilities.
- Establish the tools and mechanisms needed to encourage the reporting of existing security weaknesses and incidents, in order to minimize their effects and prevent them from recurring.
Professionalism
- Determine the competence required of staff to carry out work that affects Information Security.
- Ensure that people are competent on the basis of appropriate education, training or experience.
- Demonstrate, through the necessary documented information, the competence of staff in Information Security matters.
This Policy applies to all staff of COMPUTER GLOBAL SOFTWARE, S.L. and to external staff who perform tasks within the company.
HR will include information security duties in employee job descriptions, inform all staff it hires of their obligations regarding compliance with the Information Security Policy, manage Confidentiality Commitments with staff and coordinate user training tasks regarding this Policy.
The Information Security Management System Manager (RSEG) is responsible for monitoring, documenting and analyzing reported security incidents, as well as communicating them to the Information Security Committee and to information owners.
The Information Security Committee will be responsible for implementing the means and channels necessary for the Information Security Management System Manager (RSEG) to handle reports of incidents and system anomalies. The Committee will also be kept informed, oversee the investigation, monitor the evolution of the information and promote the resolution of information security incidents.
The Information Security Management System Manager (RSEG) will take part in preparing the Confidentiality Commitment to be signed by employees and third parties performing duties at COMPUTER GLOBAL SOFTWARE, S.L., in advising on the penalties to be applied for non-compliance with this Policy and in handling information security incidents.
All staff of COMPUTER GLOBAL SOFTWARE, S.L. are responsible for promptly reporting any information security weaknesses and incidents they detect.
7. Authorization and access control to information systems
The purpose of controlling access to information systems is to:
- Prevent unauthorized access to information systems, databases and information services.
- Implement security in user access through authentication and authorization techniques.
- Control security in the connection between the COMPUTER GLOBAL SOFTWARE, S.L. network and other public or private networks.
- Review critical events and the activities carried out by users on the systems.
- Raise awareness of their responsibility for the use of passwords and equipment.
- Ensure information security when laptops and personal computers are used for remote work.
8. Protection of facilities
The objectives of this policy are to:
- Prevent unauthorized access, damage and interference to the premises, facilities and information of COMPUTER GLOBAL SOFTWARE, S.L.
- Protect the critical information processing equipment of COMPUTER GLOBAL SOFTWARE, S.L. by placing it in protected areas, secured by a defined security perimeter, with appropriate security measures and access controls. Also, provide for its protection while being moved and while it remains outside the protected areas for maintenance or other reasons.
- Control environmental factors that could impair the proper operation of the computing equipment that holds the information of COMPUTER GLOBAL SOFTWARE, S.L.
- Implement measures to protect the information handled by staff in the offices, in the normal course of their usual tasks.
- Provide protection proportional to the risks identified.
This Policy applies to all physical resources related to the information systems of COMPUTER GLOBAL SOFTWARE, S.L.: facilities, equipment, cabling, files, storage media, etc.
The Information Security Management System Manager (RSEG), together with the Information Owners as appropriate, will define the physical and environmental security measures for the protection of critical assets, on the basis of a risk analysis, and will oversee their application. They will also verify compliance with physical and environmental security provisions.
The heads of the different departments will define the levels of physical access of COMPUTER GLOBAL SOFTWARE, S.L. staff to the restricted areas under their responsibility. Information Owners will formally authorize off-site work involving information about their business for COMPUTER GLOBAL SOFTWARE, S.L. employees when they consider it appropriate.
All staff of COMPUTER GLOBAL SOFTWARE, S.L. are responsible for complying with the clear screen and clear desk policy, to protect information related to day-to-day work in the offices.
9. Acquisition of products
The different departments must make sure that ICT security is an integral part of every stage of the system lifecycle, from its conception to its decommissioning, including development or acquisition decisions and operational activities. Security requirements and funding needs must be identified and included in planning, in requests for proposals and in tender specifications for ICT projects.
In addition, information security will be taken into account in the acquisition and maintenance of information systems, limiting and managing change.
The information systems development and acquisition policy is set out in the document: Op.pl.3.1 Acquisition of new components.
10. Security by default
COMPUTER GLOBAL SOFTWARE, S.L. considers it strategic for the organization that processes integrate information security as part of their lifecycle. Information systems and services must include security by default from their creation to their decommissioning, with security included in development and/or acquisition decisions and in all operational activities, establishing security as a comprehensive, cross-cutting process.
11. System integrity and updating
COMPUTER GLOBAL SOFTWARE, S.L. is committed to guaranteeing system integrity through a change management process that controls the updating of physical or logical elements by requiring prior authorization before they are installed in the system. This assessment will be carried out mainly by ICT systems management, which will evaluate the impact on system security before making changes and will control, in a documented manner, those changes assessed as significant or as having implications for system security.
Periodic security reviews will assess the security status of the systems in relation to manufacturers’ specifications, the vulnerabilities and the updates that affect them, reacting diligently to manage risk in light of their security status.
12. Protection of stored information and information in transit
COMPUTER GLOBAL SOFTWARE, S.L. establishes protection measures for the security of information stored or in transit through insecure environments. Insecure environments include laptops, personal assistants (tablets), mobile phones, peripheral devices, information media and communications over open networks or with weak encryption.
13. Prevention with respect to interconnected information systems
COMPUTER GLOBAL SOFTWARE, S.L. establishes protection measures for Information Security, especially to protect the perimeter, in particular if it connects to public networks, and especially if these are used wholly or mainly for the provision of electronic communications services available to the public.
In all cases, the risks arising from the interconnection of the system, through networks, with other systems will be analyzed, and its connection point will be controlled.
14. Activity logs
COMPUTER GLOBAL SOFTWARE, S.L. will log user activities, retaining the information needed to monitor, analyze, investigate and document improper or unauthorized activities, making it possible to identify the person acting at any given time.
The main objectives of Incident Management are to:
- Establish a system for detecting and reacting to malicious code.
- Have procedures in place for managing security incidents and weaknesses detected in the elements of the information system. These procedures will cover detection mechanisms, classification criteria, analysis and resolution procedures, as well as the channels for communication with stakeholders and the recording of actions taken. This record will be used for the continuous improvement of system security.
- Ensure that IT services return to optimal performance.
- Reduce the potential risks and impacts the incident may cause.
- Safeguard the integrity of the systems in the event of a security incident.
- Communicate the impact of an incident as soon as it is detected in order to raise the alarm, and implement an appropriate business communication plan.
- Promote business efficiency.
15. Business continuity
To guarantee business continuity, COMPUTER GLOBAL SOFTWARE, S.L. establishes measures so that systems have backups, and establishes the mechanisms necessary to guarantee continuity of operations in the event of loss of the usual means of work.
16. Continuous improvement of the security process
COMPUTER GLOBAL SOFTWARE, S.L. establishes a process for the continuous improvement of information security, applying the criteria and methodology set out in international standards such as ISO 27001.
17. Documented information and information classification
The specific guidelines for document management, including the structuring of the system’s security documentation, its management and access, as well as the information classification policy, are defined in Mp.info.2 Documented information.
18. Management of personal risks (GDPR)
COMPUTER GLOBAL SOFTWARE, S.L. is firmly committed to regulatory compliance, integrating the management of personal risks as a fundamental pillar of its security policy. This is in line with Regulation (EU) 2016/679 of the European Parliament and of the Council of April 27, 2016 on the protection of natural persons with regard to the processing of personal data and on the free movement of such data, and repealing Directive 95/46/EC (General Data Protection Regulation, GDPR), as well as with Ley Orgánica 3/2018, of December 5, on the Protection of Personal Data and Guarantee of Digital Rights (LOPDGDD). The company implements proactive measures to identify, assess and mitigate risks that may affect both its employees and its operations, ensuring a safe and protected work environment. This strategy not only safeguards the physical and emotional integrity of staff, but also strengthens the resilience and sustainability of its business processes.